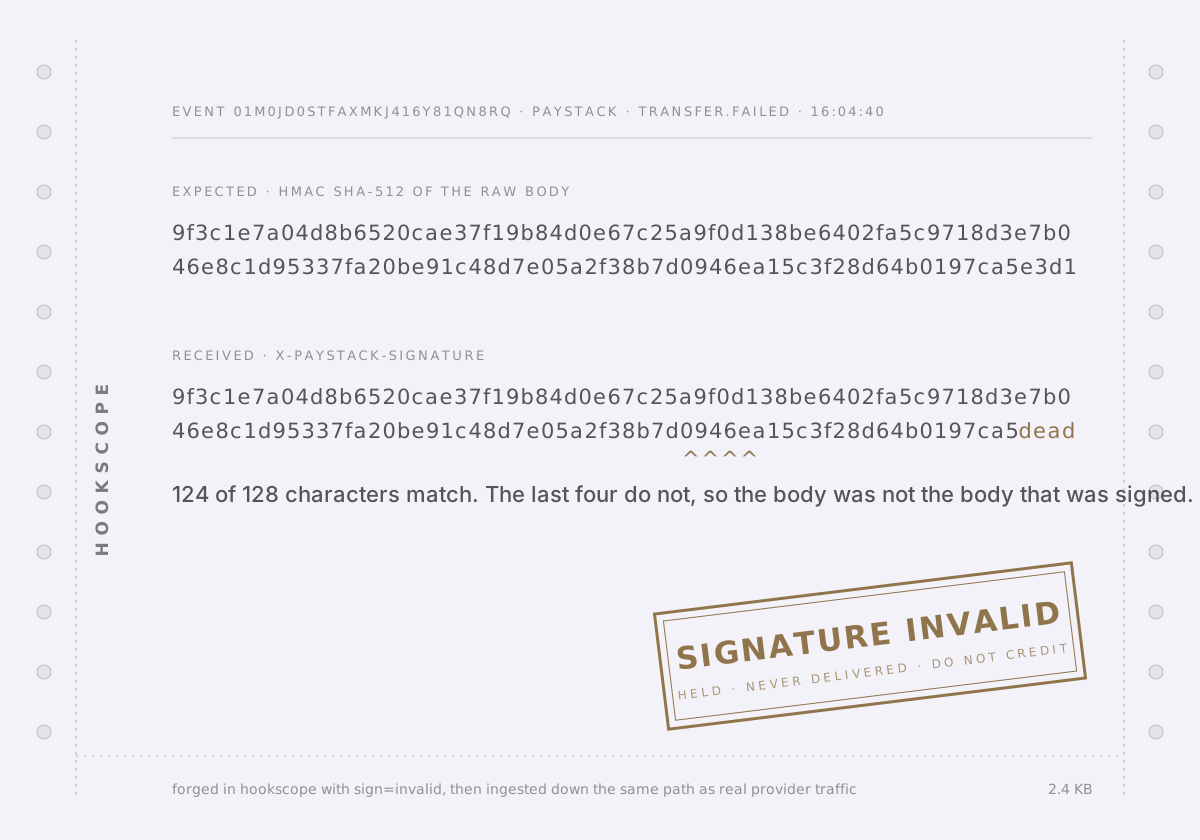
Wiring a payment webhook fails in three ways no provider dashboard can show you. You cannot see what actually arrived, only that the provider claims it delivered. Signature verification fails silently, and a genuine forgery looks identical to an honest mistake - Paystack signs the raw bytes, so parsing the JSON before hashing breaks it. And the branch that loses real money, transfer.failed, is the one branch you cannot trigger on demand. hookscope is a bench for all three. Point a provider at a throwaway URL and every delivery lands on a live timeline with its raw body, its headers, and a signature verdict that explains what the verdict actually means. Replay any capture at your own server, each attempt queued, retried on backoff, and recorded with its status, response and duration. Or forge provider-accurate payloads - signed correctly, tampered with, or unsigned - and push them through the exact same ingest path as real traffic, because a forge that took shortcuts would make the timeline lie to you. Built on Bun with zero runtime dependencies: Postgres, Redis, the HMAC, the SSE timeline and the delivery queue all come out of the standard library, and the console is three static files with no build step. The live bench runs on a free tier, so the first visit after a quiet spell can take up to a minute to wake.
- Web Dev
- Live
- Live on the web
- Live Webhook Capture · Signature Verdicts · Replay To Your Own Server · Forged Failure Payloads
Live SSE timeline, raw bytes preserved so HMAC verification stays byte-exact
Verdicts of valid, invalid, missing or unverifiable, each one explained
Replay to any target: Redis-backed queue, retry backoff, per-attempt records
Forges signed provider payloads through the same ingest path as real traffic